
The increasing reliance on technology in the UK has heightened the need for robust IT and business mobile security. Recent legislation requires organisations to reassess their security practices and compliance measures. Understanding how these laws affect IT and mobile operations is essential for safeguarding sensitive data and meeting regulatory demands.
UK businesses now face complex requirements around data protection, device usage, and digital infrastructure security. Many companies turn to IT Consultancy for guidance on navigating laws that address both fixed IT systems and mobile solutions. As regulatory oversight intensifies, organisations must distinguish between industry best practices and mandatory legal obligations to keep operations compliant, especially when working with third-party providers.
Key data protection laws shaping IT and mobile security
The Data Protection Act 2018 and UK GDPR create a legal framework that all organisations must follow when managing personal and business data. These laws apply equally to information held on internal systems and business mobile devices. Companies must ensure data is processed lawfully, individuals’ rights are protected, and data remains secure whether accessed through desktops, cloud platforms, or mobile networks.
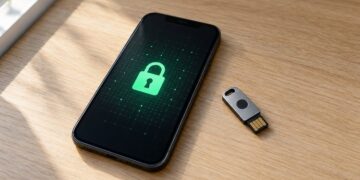
These regulations highlight strict requirements for confidentiality, integrity, and availability of information. Implementing robust encryption on both company servers and mobile devices, carrying out regular security reviews, and keeping comprehensive records of data processing activities are fundamental for meeting these legislative obligations.
Beyond the foundational requirements, organisations must also consider sector-specific regulations that may impose additional obligations on IT and mobile security practices. Financial services, healthcare, and legal sectors often face enhanced scrutiny and stricter standards for data handling. Businesses operating across multiple sectors need to map their compliance requirements carefully, ensuring that mobile devices accessing sensitive information meet the highest applicable standard. Regular compliance audits and documented risk assessments help demonstrate due diligence and can provide valuable evidence of good governance should regulatory investigations arise.
Organisations must also establish clear policies for data retention and deletion across all IT infrastructure and mobile devices. UK GDPR mandates that personal data should not be kept longer than necessary for its intended purpose, requiring businesses to implement automated deletion protocols and regular data audits. Mobile devices present particular challenges in this area, as employees may store copies of business information locally or in personal cloud accounts. Comprehensive mobile device management solutions combined with user education programmes help ensure that data lifecycle requirements are met consistently across the entire technology estate, reducing the risk of non-compliance penalties.
Incident response and business mobile considerations
When a data breach or cyber incident impacts IT systems or mobile devices, UK legislation imposes immediate notification duties. Businesses must inform the Information Commissioner’s Office about certain breaches and, where appropriate, notify individuals whose data could be at risk.
Mobile security adds another layer to incident response planning. Organisations should understand which information their business mobile provider and other technology partners can supply following an incident. Quick access to device logs, access history, and network data is critical for both regulatory reporting and internal investigation, making collaborative processes with providers an essential part of compliance.
Shared responsibility and governance for IT and mobile security
Recent UK laws and industry frameworks, including ISO/IEC 27001, emphasise that organisations and their technology providers share security responsibilities. While external partners supply platforms and support, the business remains accountable for access management, device controls, and user training.
This shared responsibility requires clear internal governance and well-defined procedures for managing both central IT and mobile operations. Regular policy updates, ongoing staff awareness campaigns, and documented supplier agreements are necessary to demonstrate compliance and reduce the risk of misunderstanding security roles.
Managing contracts, third-party risk, and ongoing compliance
Governance also extends to how businesses negotiate contracts with IT support firms or mobile service vendors. It is important to review agreements for clauses on data protection, response times, encryption standards, and transparency around sub-contractors. Ensuring suppliers meet legal requirements can prevent compliance gaps and operational vulnerabilities.
Despite outsourcing certain services, ultimate responsibility for protecting company and customer data always remains with the business. Sustained oversight, continuous risk assessments, and regular audits help guarantee that information handled on both fixed and mobile systems aligns with legislative expectations and best practices for UK security.

David Prior
David Prior is the editor of Today News, responsible for the overall editorial strategy. He is an NCTJ-qualified journalist with over 20 years’ experience, and is also editor of the award-winning hyperlocal news title Altrincham Today. His LinkedIn profile is here.